
Truecaller
Checks the sender ID, not the message content. Every lookup pings their servers. Your call metadata is the product.
“Built like a terminal. Trusted like a vault.”
Your phone, your data, your defense — Defendra detects scams in real-time, fully offline, fully private.
View source on GitHub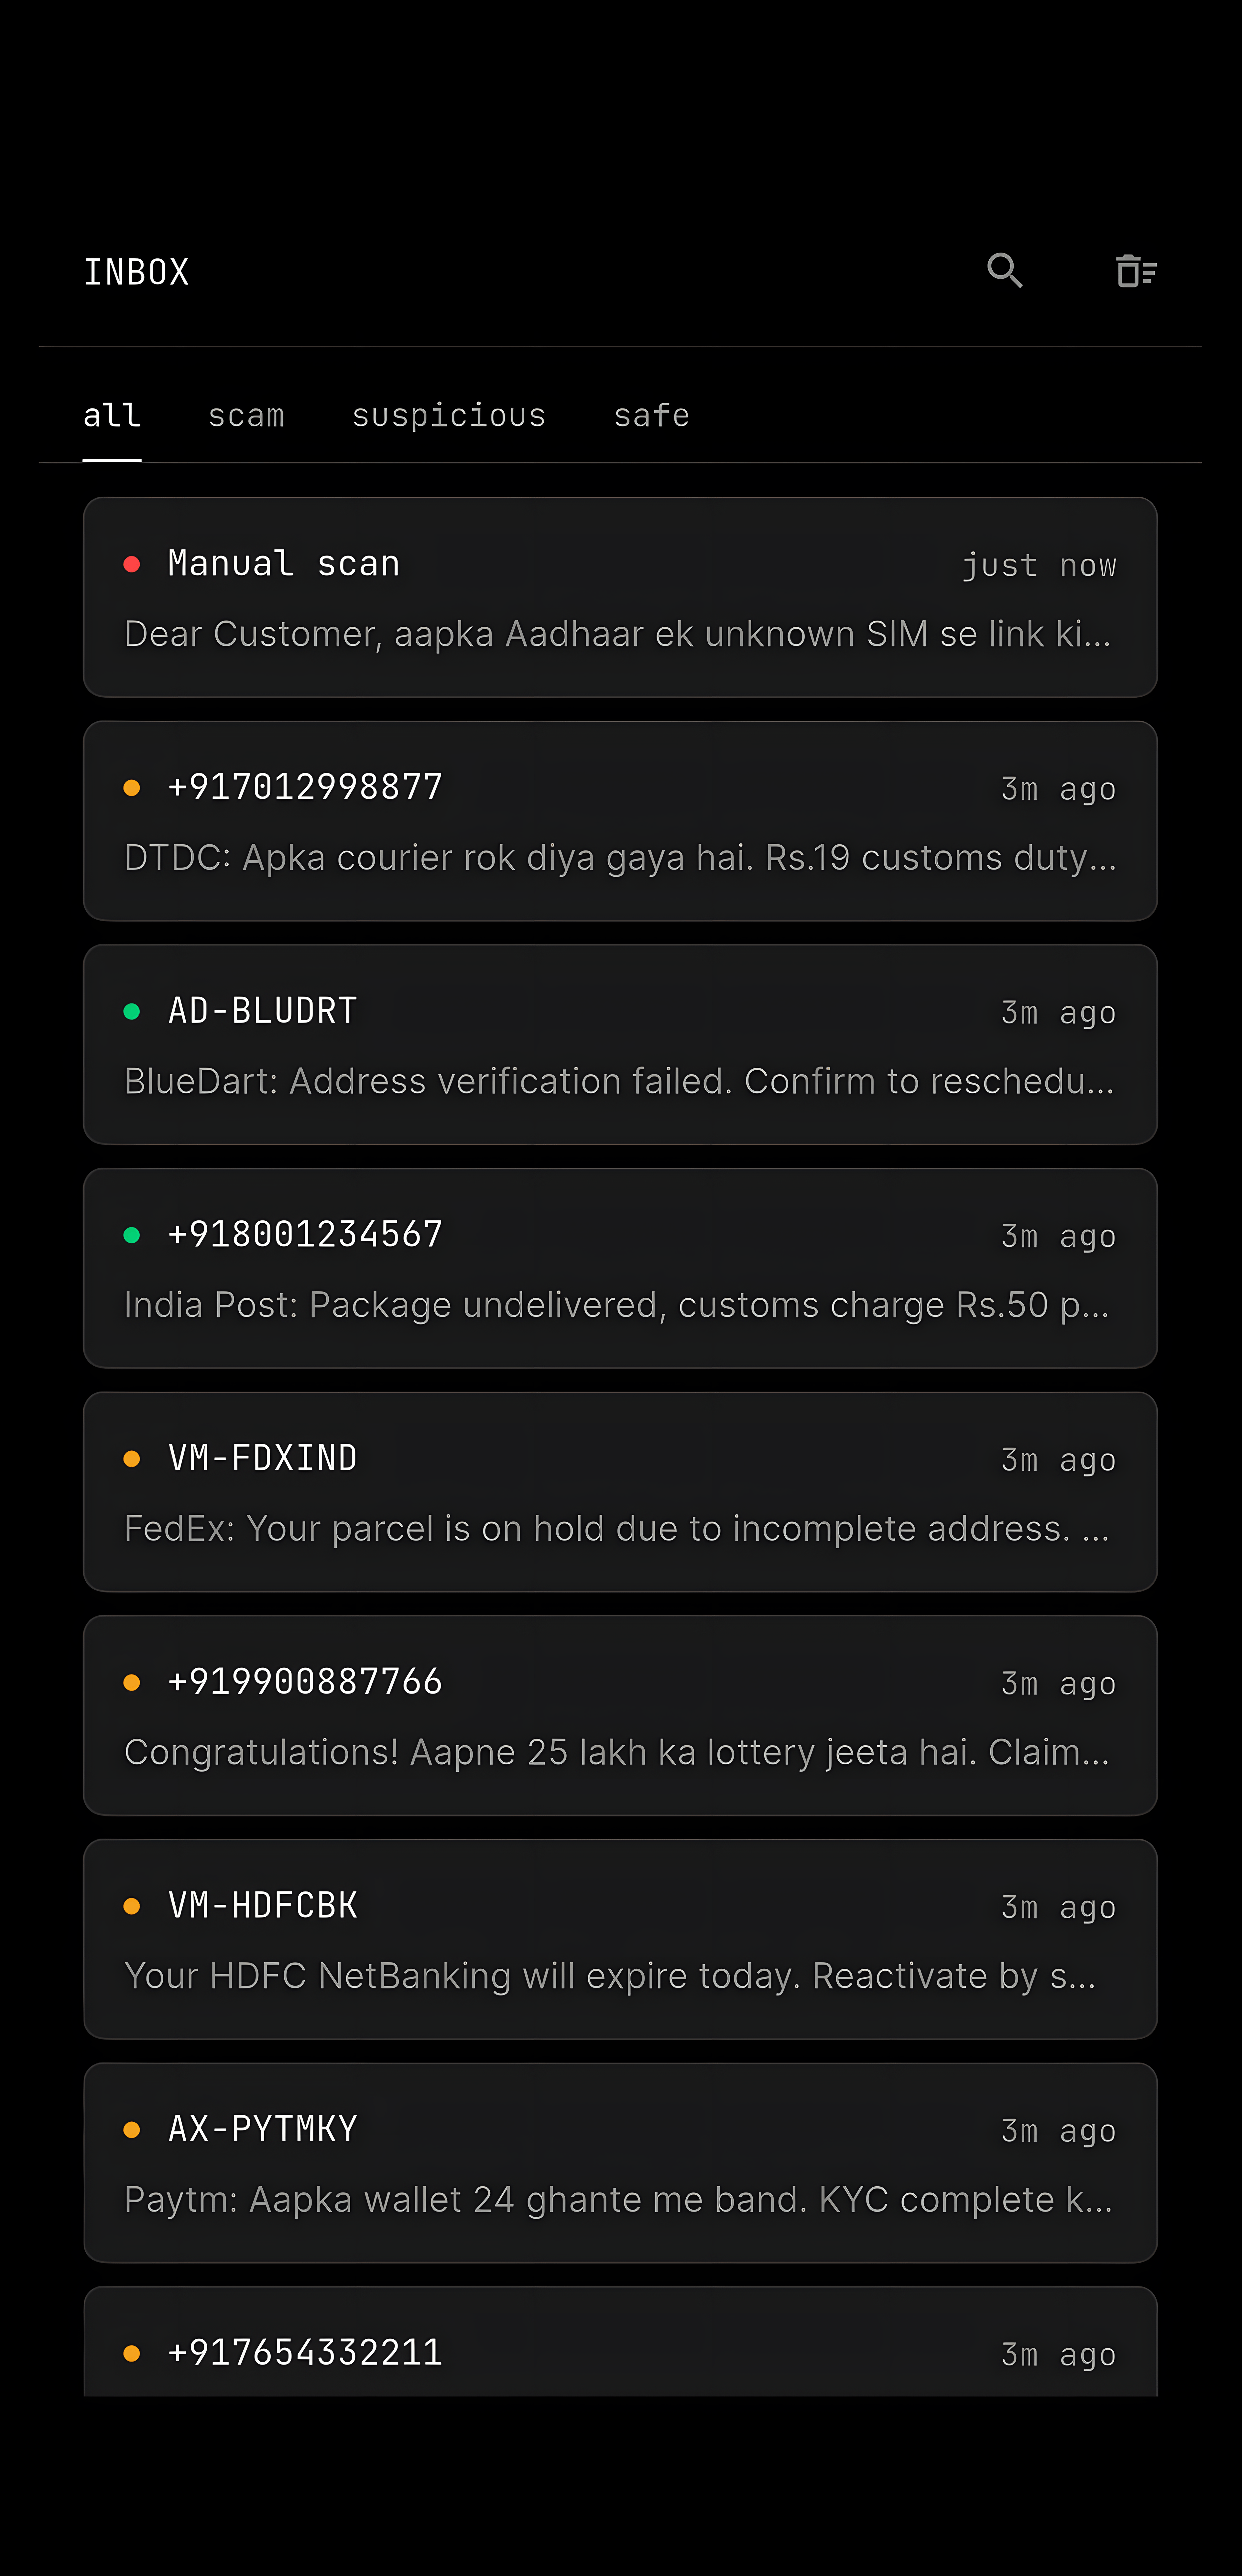
The existing defenses weren’t built for this threat model. They’re reactive, data-hungry, or both.
Checks the sender ID, not the message content. Every lookup pings their servers. Your call metadata is the product.
Fraud alerts trigger after the transaction clears. They're logging incidents. Prevention isn't the model.
Blocklists are updated in days. Scam campaigns mutate in hours. The gap between is where you get hit.
Android delivers the incoming message to Defendra before your default SMS app sees it. No network request is initiated.
A fine-tuned DistilBERT-multilingual model tokenizes and classifies the full message body — entirely within the app sandbox.
The model outputs SAFE, SUSPICIOUS, or SCAM with a probability score. No blocklists. No heuristics. Pure model inference.
The exact phrases that drove the decision are highlighted in the UI. You see the reasoning, not just the label.
No network call, ever. The model binary ships in the APK. Analysis is local. Results are local.
Most apps promise privacy. We don’t have a choice — there’s no server to send data to.
That’s not a promise, it’s a constraint.
Every verdict surfaces the trigger phrases that drove the decision. You know exactly why a message was flagged.
Your OTP for HDFC Bank is 847291. Do NOT share it. However, your account shows suspicious login. Verify now: bit.ly/hdfc-secure or call 9876540011 immediately.
Mimics a legitimate bank OTP SMS while injecting a phishing link and phone number — a dual-vector attack designed to steal the OTP and redirect the victim to a vishing call.
No. Defendra requests no network permissions from Android. The TensorFlow Lite model runs entirely on-device. Your messages are never transmitted, logged remotely, or stored outside the app's own sandbox. You can verify this by inspecting the APK or reading the source.
Google's SMS permission policy requires apps with broad SMS access to be set as the device's default SMS app — a restriction that would compromise the UX. Rather than workaround or fight it, Defendra ships via F-Droid and direct APK download. This is an honest constraint, not a red flag.
English, Hindi, and Hinglish (code-switched Hindi/English). The base model is DistilBERT-multilingual. Training data includes Indian scam patterns across all three registers, sourced from public datasets and manually collected examples.
The v0.1 model achieves ~91% precision and ~87% recall on a held-out test set drawn from Kaggle India SMS datasets, synthetic scam variants, and real-world examples. With your consent, local misclassification data is used to improve future versions — nothing is uploaded.
Free, open source, and offline. No account. No permissions beyond SMS. Ships as a direct APK.
View source on GitHub